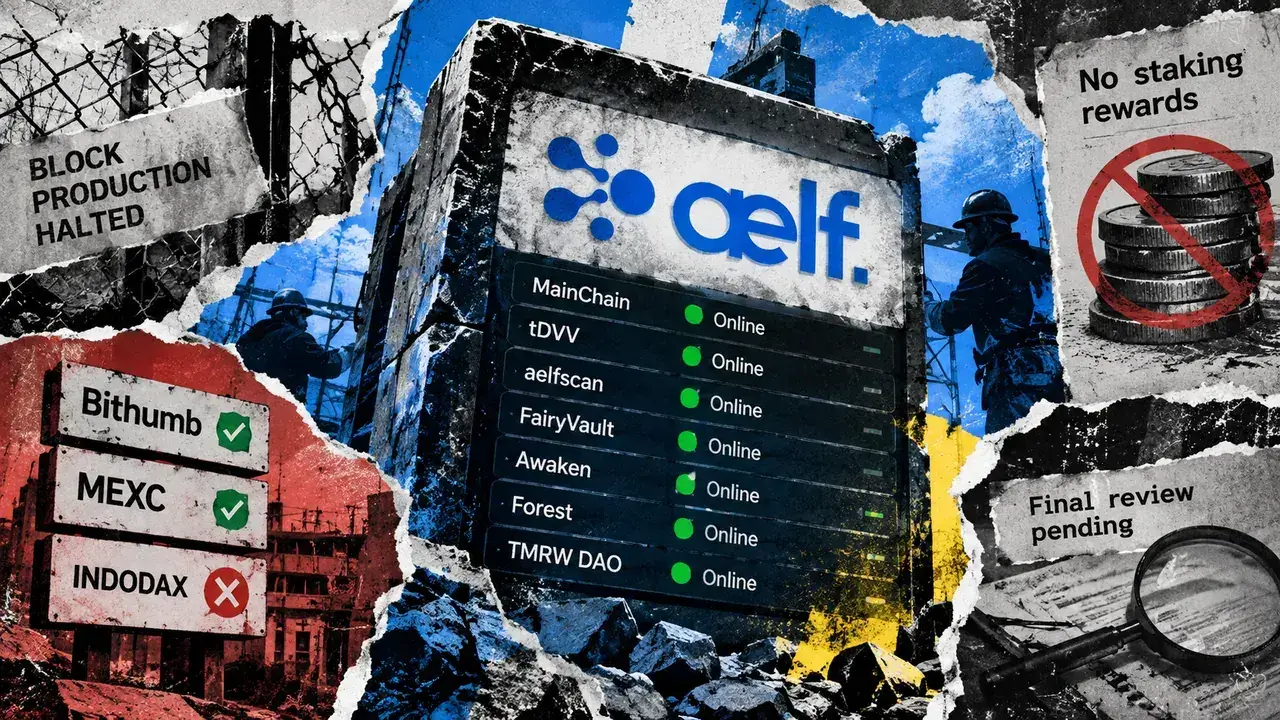
aelf, a blockchain network built around its AELF MainChain and tDVV dAppChain, has restored public node access and several core services after malicious smart-contract activity led to a controlled recovery. The incident halted block production for approximately one week, and the reopening remains incomplete.
The project's Sept. 14 recovery update said both public nodes were available again, alongside the aelfscan explorer, FairyVault transfers, Awaken trading, Forest NFT browsing and the TMRW DAO staking interface. On Sept. 15, the MainChain and tDVV status endpoints were reachable with advancing block heights, though those checks did not test whether users could submit transactions.
The aelfscan, FairyVault, Awaken, Forest and TMRW DAO frontends were also reachable. No end-to-end transfer, trade or reward claim was executed during those checks.
Ontology forces urgent node upgrade after restarting chain hit by malicious activity
What remains incomplete
aelf said exchange deposits and withdrawals were resuming gradually and could differ by venue. Bithumb's updated notice scheduled ELF deposits and withdrawals to restart on Sept. 14 at 14:00 KST. MEXC scheduled its resumption for Sept. 5 and told users to generate new deposit addresses because previous ones were invalid. These announcements set venue schedules but do not prove live account-level availability.
INDODAX's Sept. 2 notice, meanwhile, still described ELF wallet deposits and withdrawals as closed. Because that notice is dated, it may not reflect a later change in account access, reinforcing the need for users to check each venue before moving funds.
The block-production pause also had a direct staking consequence. aelf said no network staking rewards were generated during the approximately one-week halt. Restoring the TMRW DAO interface does not change that outcome: there are no network rewards from the halted period to claim.
aelf's Aug. 26 incident update said investigators had identified 155 transactions associated with the malicious activity, including 127 on AELF and 28 on tDVV. It also described five unique .NET assemblies capable of interacting with host systems and node-related keys and configuration, raising risks beyond the smart contracts themselves.
aelf cautioned that those capabilities did not prove every payload executed, every targeted credential was obtained or data was successfully transmitted. Its evidence review had found no unauthorized transfers of ordinary users' assets or exposure of ordinary-user wallet keys as of Aug. 26, but that conclusion explicitly excluded unresolved node and infrastructure credential exposure.
The full post-incident review, technical appendix and final root-cause assessment remain unpublished. aelf said those materials would follow after the remaining work, including an independent review, is complete. Until then, restored services mark operational progress, not a final security all-clear.
The post 7-day blockchain outage wipes out a full week of staking rewards after emergency aelf shutdown appeared first on CryptoSlate.

Comments (0)
Please sign in to comment.
No comments yet. Be the first to comment.